Unnoticed sharing
Identity, contact or financial information left inside a document can be shared inside or outside the organization without anyone noticing.
Developed on PaperWorkAI, ISDD (Intelligent Sensitive Data Discovery) uses AI to automatically detect and mask personal data in electronic documents and image files, and secures document access based on each user’s permissions.
When a document is opened, authorized users can see the information they need, while users without permission see the same document masked. Organizations manage document-level sensitive data security with a centralized, automated structure.
Customer Information Form
MaskedNote: The same document looks different depending on the user’s permissions. People who do not need the data do not see the sensitive fields.
Identity, contact or financial information left inside a document can be shared inside or outside the organization without anyone noticing.
An employee with the right to access a document can also see personal data on the same screen that they should not see.
Building document security separately in ERP, CRM, HR and legal applications becomes costly over time.
Opening and checking thousands of documents one by one is not sustainable. As workload grows, so does the risk of error.
High operational burden, penalties, reputational damage and audit risk in KVKK compliance
Detected fields
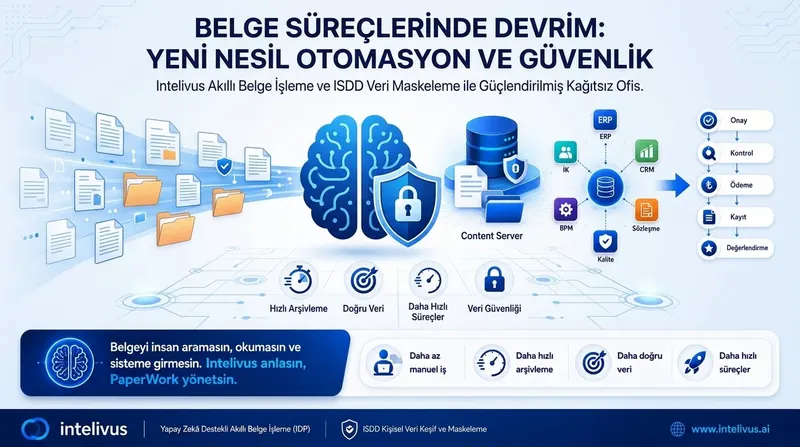
In organizations, documents are not created in a single place. HR documents may come from HR systems, invoices from ERP, customer files from CRM, contracts from legal processes and application forms from portals.
Masking separately in each application is both costly and hard to manage. And as systems multiply, data security control weakens. ISDD works with PaperWork Document Management to analyze and mask documents centrally.
The result: lower operational burden, stronger KVKK compliance, more secure document access and centralized control.
Works on Office documents (Word, Excel and PowerPoint), PDFs, scanned documents and image files. Even when documents come from different sources, the masking approach stays the same.
The same document is shown differently based on the user’s role. People who do not need sensitive data see the part of the document required for their work; personal fields are masked.
Documents from different applications are analyzed in one central place. Even as the number of applications grows, the masking standard stays consistent.
Organizations can add terms they consider sensitive for their industry. ISDD treats these terms like personal data.
ISDD can work inside PaperWork and can also process documents from other applications as a service. The application sends the document, ISDD masks the personal data and returns a secure output. A shared masking service can be used without changing the existing application architecture.
Plug-and-play setup: ISDD is a flexible, practical solution that can be rolled out quickly. It can start working without long customization projects.
HR documents can contain fields such as identity, address, phone, family information, bank account and signature in the same file. ISDD detects these fields within the document; the HR officer sees the required data in clear, while other users involved in the process see the sensitive fields masked.
How does the flow work in this scenario?
Documents that legal teams work with can contain party information, addresses, identity data and expressions the organization considers confidential. ISDD does not leave security to folder permissions alone; it also manages the sensitive fields inside the document.
How does the flow work in this scenario?
Finance documents can contain IBANs, tax information, signatures, and customer and supplier details. ISDD finds these fields automatically and provides controlled visibility during archiving, approval and sharing.
How does the flow work in this scenario?
Application forms, request attachments, identity documents and customer correspondence come in through different channels. By masking these documents centrally, ISDD prevents customer data from circulating uncontrolled between teams.
How does the flow work in this scenario?
ISDD manages this risk automatically at the document level. It finds personal data with AI, masks it based on user permissions, provides centralized document security and strengthens the organization’s KVKK compliance processes.
Stop checking documents one by one. Secure sensitive personal data automatically with ISDD.
ISDD is an AI-powered automatic document masking solution developed on PaperWorkAI. It detects personal data in electronic documents, PDFs, scanned documents and image files, and masks it based on the user’s permissions.
It reduces the risk of personal data in documents being viewed or shared unnoticed, or becoming accessible to unauthorized people. It eliminates the need for manual masking and provides centralized, automatic document security.
By automatically detecting and masking personal data in documents, it helps prevent unauthorized viewing. This makes organizations’ personal data security, access control and audit processes more systematic.
By preventing sensitive personal data in documents from being exposed uncontrolled, ISDD helps significantly reduce penalty and compliance risk. However, KVKK compliance requires many elements to be managed together, including processes, policies, authorization, records management and audits.
It can be used on Office documents (Word, Excel and PowerPoint), PDF files, scanned documents, image files and documents coming from various enterprise applications.
No. ISDD can show documents masked or unmasked based on the user’s permissions. Users who are not authorized to see personal data view the document in masked form.
Yes. Organizations can define terms they consider sensitive due to their industry or internal policies. ISDD treats these terms like personal data and masks them automatically.
No. ISDD can work as part of the PaperWork platform and can also be used as a service. It can receive documents from different applications, mask them and send the result back to the relevant system.
Instead of masking separately in different applications, documents are analyzed and masked in one central place. This approach reduces operational workload, increases control and creates a sustainable KVKK compliance structure.
With ISDD, automatically find sensitive data, mask it based on user permissions and manage documents from different applications in a centralized structure. Review your organization’s document sources, permission structure and masking needs together with the PaperWork team.
We find a time that suits you.
We hold an introductory meeting.
We run a demo tailored to you.